Exciting News! We are transitioning from Cyber909 to 909Exec.

Richard Bird, a 25-year cybersecurity veteran and former Global Head of Identity at JP Morgan Chase, joins Den Jones to deliver a frank, data-driven indictment of how cybersecurity has been measuring the wrong things for decades.
EPISODE TITLE: Built Wrong: Why Cybersecurity Is Failing and What We Must Do About It
DESCRIPTION:
Richard Bird, a 25-year cybersecurity veteran and former Global Head of Identity at JP Morgan Chase, joins Den Jones to deliver a frank and data-driven indictment of how the cybersecurity industry has been measuring the wrong things for decades. The conversation digs into why spending more money on security has not made organizations safer, what three metrics actually matter, and how the industry can begin to rebuild on a foundation of outcomes rather than activity. This is a rare, unfiltered debate that challenges vendors, practitioners, executives, and regulators alike.
GUEST INFORMATION:
EPISODE HIGHLIGHTS:
[00:02:46] - Richard Bird's Background and Career Journey
[00:04:29] - Announcing the Book: Built Wrong
[00:07:45] - The Trigger: The Hacker in a Hoodie Index
[00:10:17] - Measuring Activity Instead of Outcomes
[00:12:22] - The Myth of the Sophisticated Adversary
[00:15:42] - Security People Should Stop Using the Word Risk
[00:18:40] - The Self-Perpetuating Mythology of Cybersecurity
[00:24:08] - The Three Things That Actually Need to Be Measured
[00:28:50] - Compliance Frameworks and the Problem of Outdated Controls
[00:30:33] - Where Cybersecurity Came From: The IT Operations Origin Story
[00:39:23] - How to Fix It: The Last Third of the Book
[00:47:54] - Business Economics and Cybersecurity as a Real Business Function
[00:52:57] - Stewardship and the Obligation to Protect
RESOURCES MENTIONED:
KEY TAKEAWAYS:
SOCIAL MEDIA QUOTES:
CALL TO ACTION:
If you found value in this episode, please subscribe to 909 Exec and leave a rating to help others discover the show. To learn more about 909 Cyber, their advisory services, and how they help organizations secure growth, visit 909cyber.com. To sign up for pre-launch updates on Richard Bird's book Built Wrong and access economic data on the adversary versus defender investment gap, visit hackerinahoodie.com. To learn more about 909 Shield, the identity proofing and biometric fraud detection product for service desks, visit 909shield.ai.
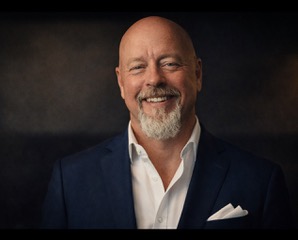
Richard Bird is Chief Strategy Officer and Chief Security Officer at Singulr AI. He has spent three decades inside the system he critiques, moving from executive roles in global banking and corporate technology into start-ups and public advocacy. He publishes The Hacker in a Hoodie Index, a live record of what cyber incidents actually cost, and is the author of three books: Famous With 12 People, the forthcoming Built Wrong: Why Cybersecurity Keeps Failing and How We Can Rebuild It, and its companion volume The Verified Security Framework. He speaks around the world to rooms that range from dinners with boards of directors to conference halls in front of thousands.


Den:
Hey folks, just before we start today's episode, I'd love to share a little bit about 909 Shield. It's our flagship product that helps you trust the human that's on the other end of the phone or the video. Think of this, right? Someone calls your service desk, they want to change their password or their MFA. They're giving you a lot of stress. You need to do it now. There's a sense of urgency. Well, your service desk people, they want to help, so they'll go reset the password. But today's process is to validate that that person is real on the other end of the line. They're just not up to the challenges of the attacks we're being faced with. 909 Shield helps protect your company and your service desk from these kind of threats by doing identity proofing, biometric and AI fraud, all wrapped into a nice little bundle.
So please, if you want to learn more, go check out 909shield.ai. Hope you enjoyed today's show. Thanks folks.
Narrator:
Welcome to 909 Exec, the executive leadership podcast from 909 Cyber where cybersecurity intersects with business strategy. Your host is Den Jones, founder and CEO of 909 Cyber. Den has been a practitioner for more than three decades, including leading enterprise security at Adobe and Cisco, helping executives navigate risk, trust, and transformation. Each episode goes beyond headlines and hype with conversations that matter to leaders shaping the world of technology. So please join us for 909 Exec episode 69 with Den Jones and Richard Bird.
Den:
Well, everybody, welcome to another episode of 909 Exec, your podcast. Hopefully it gives you some wit, wisdom, and some education in your executive journey. Every episode I bring in some fantastic guests and today we're blessed because I've been trying to get this guy on my show for, I think since episode one, and we're probably about episode 70 now. Richard Bird, good friend, mentor, confidant, coach, wizard in the identity space, and someone that we met a long time ago in Identity Defined Security Alliance days. Richard, welcome to the show. Love you to introduce yourself, tell us what you're up to at the moment, and then we'll dig into some fun topics.
Richard:
Well, thanks for having me on Den. It has been a struggle and I do apologize. We talk about this all the time when we see each other at conferences. I get a little sick of giving my bio because it seems like it's something I do about a dozen times a week. But a lot of folks know me in the industry, long time corporate guy. The identity chops came accidentally from being the global head of identity for JP Morgan Chase. Didn't start out that way. It was just identity for the retail bank. And next thing I know, I woke up one morning and I'm running a centralized function for about 350,000 people and 72 contractors and 2.4 million machine accounts because that's what I certified for SOX every quarter. So I did a lot of ditch digging in my career for about a quarter century, and then I moved over to the security and solutions side.
And I've been now getting ready for my fifth successive startup company. You might think that that means I can't keep a job, but the reality is that that's the way that the security startup world works. It is a fast industry and you're there to deliver for a certain part of the journey and rarely are you there for the whole journey unless you're the founder. But I've been fortunate to work with a lot of great founders, had a tremendous amount of learning that's happened. Basically, I'm always like, I'm in the third stage of my career. I'm learning something new every day, being a part of the startup community, being a part of the venture capital community, being a part of standards communities, none of which were things that I was ever exposed to prior to about 2018, 2019. So I get to learn everything all over again.
And that learning's kind of brought me to a point where what's been going on lately is I apparently have lost my mind. I decided not to write one book. I decided to write two books. I swore I would never write an industry book. These are industry books. And the core book is titled Built Wrong: Why Cybersecurity is Failing and How We Can Rebuild It. And before people start arching their backs and getting a little red in the face, this is a love letter to my community where I'm doing what I believe is one of the first systemic diagnoses of cybersecurity ever attempted, which in itself is crazy. I tackle everything, vendors, cyber insurance, corporations, you name it. Nothing is out of bounds relative to what is challenging the cybersecurity community today to deliver performance and outcomes, not measure activity. The most important thing that I'm trying to answer with this book is are we getting safer today versus where we were yesterday?
And if we're not, that opens up a lot of questions about what we're investing in and what we're measuring, and that's probably what we're going to dive into in this conversation.
Den:
Yeah. So I admit that I'm not really much of a reader. You did send the book out to a select core group of people for proofreading and feedback and all of that good stuff. And I know from speaking to others that people are pretty impressed with this book. This kid though, being not one for reading, I was eating some humble pie when we met at Black Hat this year, admitting my feelings and apologizing for not really doing you justice. So it's on the record. I like audiobooks, so I'm waiting on the audiobook or the movie. Maybe the movie will come out.
Richard:
Well, I get to work on the audiobook script actually probably today or tomorrow. And I'm now targeting, and it's probably worth sharing up front, we'll share it at the end, I'm now targeting around the mid to end of October for the release of the core book. I will say the second book actually is all the metrics and measures that are associated to performance and outcomes that we're not using today. That has been, if you're not a reader, I'm not a math guy. And to build metrics and measures has been really, really challenging. I mean, in that particular case, thank God for AI because it's been extremely helpful, but I realize that that particular book needs eyes from general counsels and accountants, CPAs, CFOs that will probably extend the release date of that book by about another three to four months. But people will have enough to digest with the core book itself once we get it out in October.
Den:
So let's talk about, well, a couple of things. One is what was the trigger that made you think I'm going to do a book? I mean, because we talk about this shit all the time about there's a million books out there, so why now and what was that impetus?
Richard:
Well, I think the why now part was is it's already too late in terms of changing the current state trajectory of cybersecurity performance. This is not Richard's opinion. We can look at the FBI IC3 report just on reported cyber losses just in the United States, and that's a figure that's grown by a 35% compound average growth rate between 2014 and 2024. That means the bad guys are doing six times better on the invested dollars that they're using to attack things than we're doing on the dollars that we're spending to protect things. So that actually came from a story I was telling on stage. And again, you know me and my speaking style, whatever the slide might be up on the screen, it could be what I'm talking about. It most likely is not. And I was presenting a number of years ago at Identiverse, and this is back for people that are not old enough to remember this, this is back before you had Gamma and Claude and ChatGPT build your PowerPoint presentations for you.
We actually had to, I mean, this goes way back like three years ago. We had to actually go out and find pictures to put in our PowerPoint presentations and hope that they were royalty free or do screenshots and hope that nobody noticed.
Den:
Or not give a shit.
Richard:
Or not give a shit. And so I'm cutting out pictures for this PowerPoint and for the life of me, I cannot find a picture on the internet of a hacker who isn't wearing a hoodie. And so I get up on stage and not thinking about this reality and I'm waving my hand at the PowerPoint presentation and I said, "Look, anybody in the audience, have you ever seen a picture of a hacker without a hoodie?" And everyone got a good chuckle, right? And I was like, "I wonder, if I invested $100 in a hacker 20 years ago, and I now hate using the word hacker and we'll talk about that in just a second, but if I invested $100 in an adversary 20 years ago, how much more money would I have made than investing in the stock market?" And that was it. And that kind of went in a drawer for a while and then all of a sudden it popped back up in a number of conversations over the next year or two.
And the book is actually a compilation of almost all of my speaking engagements, presentations, white papers from the last decade. I didn't actually have to write a book. I just had to sit here and tell myself a story and start typing. And when I got to this realization of everything in the capitalist and socialist economies around the world measure things with dollars, except cybersecurity, we don't measure things with dollars. We don't measure things with economic or financial mathematics at all. We measure activity. And so I was like, "Well, I wonder how we're doing as good guys against the adversaries if I did invest that hundred dollars." And that created this thing called the Hacker and Hoodie Index. And that became this just boulder coming down the mountain of momentum of like, oh my gosh, not just the dollar figures, where the hell did this hacker in a hoodie mythology come from?
Anybody that's worked for any number of years in the industry knows that this is not what hackers look like. They are not in neon-filled rooms with numbers cascading down the LCD, LED panel walls and hood over, can't see face. They're kids working in sim sweat shops. They're people that are working as forced labor to crack every different kind of thing that you can imagine. They are organized in war rooms and if they're not physical, they're virtual. So where did this myth come from? And the myth came from our own telling of the story in cybersecurity along with the media and the media propagates this thing. And what does a hacker with a hoodie represent? A sophisticated adversary. And then you start to walk that back for just a second. Well, wait a minute. All of the numbers and all I do is rely on published numbers.
I am not making anything up with this book. All the numbers show clearly that the vast majority, the super majority of successful cybersecurity attacks are not novel, they're not unique, and they definitely ain't sophisticated.
Y look at the Verizon DBIR, you look at global threat out of CrowdStrike, you look at it is the same shit every year, which is fascinating because what does that say about the cybersecurity ecosystem? We can't even fix the problems that we know about. The ones that have been broadcasted to us every year, hundreds of thousands of breaches and exploits every single year, and we haven't improved on a single one. And that takes us back to the FBI IC3 report. We went from 800 million to over $21 billion in 10 years in recorded cyber losses. All wow, cybersecurity spending grew every single year in that same span. We're spending more money and losing more money. This is not a business that anybody would invest in. But if I invest $100 in the hacker and a hoodie, I'd make some coin.
Den:
So you and I, we love to call bullshit on things. So I call bullshit on the fact that least privileged in all that conversation, I'm like, we have not done the basics of some of these things right. And then the other thing is somebody would do the SANS top 10 and they'll be like, okay, I've deployed these things. And to your point, measurement of success, and this really also stems from the IT world, measurement of success was I deployed the thing on the assumption of the thing is the thing that reduces the risk because my strategy slide said so. So I spun up, let's say, I've done vulnerability management program and because I do a vulnerability management program, that should reduce our vulnerabilities. And then the more money you spend on it, well, the real question is does it just find more? Am I now scanning more shit because I've got a program, which now means I find more stuff.
So the numbers of the, I deployed something, therefore for me never rings true. I think if you deploy something, it doesn't mean you reduce the risk, it just means you deploy technology, good or bad deployments, and actually the thing that's integrated with the other thing, those are levers that determine at the end of it whether you reduce the risk. And I still would hypothesize, does everybody know how to measure risks? Yeah. I mean, we talk about it as if we've fucking figured that shit out and I'm like, I don't know, man. People subjectively measure risks. And as you kind of banter back on this one, the hypothesis of the book, if you're going to give me a one sentence, what is the hypothesis, the takeaway? Is it just that we've screwed all this up and we need to rethink it? Jump into that for me.
I'll rebut all my bullshit
Richard:
Too. Yeah. Let me tackle that first because I think, like I said, building a book that questions the entire industry, the entire ecosystem, for many people will feel confrontational. And I already said it's not, it's a love letter. This profession has fed and clothed and made a very successful life for me, and I love it. That's why I continue to work in it, right? I'm not pointing fingers. What I am showing with data and evidence is a case that supports a lot of what people intuitively feel. Your risk management one is one of my favorite. Security people should not use the term risk. Now, people are going to get angry when I say that, but the reality is that security people have no idea what they're talking about when they say risk. And the reason that I know this is because in security, everything is a risk.
Vendor's a risk, supply chain's a risk, codes are risk. The reality is that risk is what is left over when you have done what you are able to. So if I have allowed persistent standing privileges and an identity that gets popped, and that is then used to encrypt my production data stores, and that is then used to leverage me in a position to have to pay or not pay a ransom, none of that was risk. That was all self-chosen. Your risk was making shitty decisions about giving people too much access. Your risk was not the bad guys. And I have this benefit of actually being a formal trained risk manager. I was trained when I was at Anderson Consulting a long time ago. I know, I read all the damn textbooks. And what people miss in security is that risk is not a technological term.
Risk is a financial term. Risk always rolls to financials, always. If it doesn't, and this is in the corporate world, if it doesn't, then it ain't a risk or you can't quantify it in the monetary or financial terms necessary to be able to tell whether you're reducing or growing risk. This is why in the vendor space, people stay with a 20-year relationship and contract with a solution provider who's become a massive part of their security architecture and have never been questioned on whether or not they're returning any kind of security yield for the money that they're being paid. Not the vendor's fault, because the vendor's just delivering exactly what the system wants. The system wants measurements of more activity, which is something that you said earlier. So think about this for a second. If I spent 30 years building a system that measures the wrong things, what do I do on the corporate side?
I begin incentivizing and rewarding people on the wrong things because that's what's coming out of the architecture and the solutions and the structure that I've built. And then as I start rewarding them, what am I going to do? I'm going to reward them for more of the wrong things without anybody ever going, "Hey man, is this shit working?" And instead, what's happened in the last 20 years is because we intuitively in security know that it's not working, we start telling these myths about ourselves. It's not a matter of if, it's a matter of when. Security people say that. We are the people that propagated that myth. And when you think about it, we are literally the only profession in the corporate world that gets up in the morning and goes, "I'm going to go to work and get my ass kicked." A CMO doesn't go, "I'm going to spend all this money and our market share is going to go down." A CFO doesn't go, "I'm going to spend all of this money and it's inevitable that I am going to miss state earnings at some point." So y'all might want to sign your get out of jail free cards right now because if we misstate earnings and it's really, really bad, we're going to the pokey.
There's nothing equivalent to the way that we have mentally established our weakness in providing security and safety in terms of outcomes and performance. We have become consumers of our own mythology and the data is all there.This book has over 110 footnotes and citations and not one of them is freaking bleeping computer. And I love those guys.
The academic information, the economic performance information, the financial information is all out there and it raises this question. First of all, in the cybersecurity industry, are we just too beaten down to be able to dig into it ourselves? So I'm the idiot to stand up for that job. I'm going to go do it. But then if we look at the rest of the industry, think about cyber insurance. Well, if I've spent 30 years building the wrong thing and measuring the wrong thing, that would suggest that premiums and policies that are currently associated with cyber incidents and events cannot possibly be right because those policies are being written based upon the core of evidence and data that's associated with this system that was built wrong. Vendors, if vendors are not building features or capabilities that prove that security is providing safer outcomes, what are they spending it on?
Providing more blinky lights and more data and more information. "Hey, can I take all this? I've lived this life for the last nine years. Can I take all the cool information contextualize out of your security solution and put it in Splunk? Why? Why? Oh, because I want better reports. "Do you want to be safer? That's kind of the more important question. If I have to swivel chair to be able to react and remediate something immediately, isn't that a lot better than waiting for a stupid report to port out next week? But this is the institution that we've built. And kind of come back to tying it off at the end, look, I'm not saying that everything needs to be burnt down. Matter of fact, the reality is that there are a lot of things that are directionally correct, except they're focused on very, very small parts of the overall system.
And this is a system problem. This is not a point problem. This is a system problem, which means if somebody's doing kick-ass work in one particular area of security, and this is very interesting, things like probability calculations that are being applied, say in intel and vulnerability space where we're trying to determine what is the likelihood that a vulnerability will be exploited as opposed to the old way of doing it of I'm just going to patch everything that comes in that's high. So what? Do you know whether or not those high vulnerabilities are actually going to remediate any risk in your organization? And there I did. I used the risk word. Do you know that it's going to reduce the likelihood of damage? And this is probably a good point to get into some conversations about this. The reality is there are only three things that need to be measured in security, and these manifest virtually nowhere on the planet currently today.
There are some exceptions, right? Exposure.
Den:
Yeah, we'll pause for a quick break though, and then when we come back, I want to dig into those three things. Okay folks. You bet, man. Back in a minute.
Hey folks, just want to take a minute to say thanks for listening to the show, watching the show, however you engage with us. If you're liking the conversations, if you think we're adding some value, we'd love you to like, subscribe, and share the show with your friends if you know of anyone else that would benefit. Ideally for us, that will help us be able to grow the show, invest more in the quality, get some more exciting guests and keep bringing you some executive goodness. Thanks everybody. Take it easy and enjoy the rest of the discussion. Hey Richard, so three things, man. So let's talk about these three things.
Richard:
Three things are the only things that you need to measure in security. Now, the math to actually do it is a little bit different, and the data's already all there. First of all, what's your exposure? I can't measure exposure. I always love this one. We don't have enough data. I'm sorry. Try working in security 15 years ago compared to the data that you have now. You can measure your exposure. You can measure your exposure pathways. How many standing and excessively privileged accesses do you have? Oh, that's really hard to go get. If the argument that we can't measure something in security is because it's really hard, we just need to close down shop and go home. Really hard is our life. This is what we do. We fight the bad guys. That's hard. So exposure, how big is your exposure? Where are your exposure pathways?
Where do you not have interdiction, number two? Where do you not have actions, tasks, triggers that you can take when the exposure is actually exploited? So we measure exposure, we measure interdiction. What are the methods? What are your control sets? By the way, spoiler alert, 80 plus percent of all controls today are identity. I didn't set out to write a book that was championing identity. I was going after everything in cybersecurity, but the reality is that right, wrong or indifferent, we have built all of our controls around identity. We treat identity like the redheaded stepsister in security because it ain't cool, it ain't sexy. And the reality is that these are where the unsophisticated breaches continue to be successful. Why? Because the interdiction to stop one person's Microsoft. I'm tracking all of these breaches and incidents on a hoodie index or hackeranahoodie.com. Every one in the last two weeks has been some employees' Microsoft email account was hijacked, and through that, they got to all core data, all customer data, all patient data.
I'll go back to that ain't a risk, that's negligence, that's malfeasance. If your entire organization come down because of one person's account, you got some serious problems that have nothing to do with your security solutions, interdiction. And the last one is consequence. And this one's been really interesting because I started writing this book three years ago and what I found is the market is proving that these are the three measures unexpectedly. Why? AI. When you look at what is happening with AI today, there's beginning to be an over rotation on containing the blast radius, resiliency, recovery. Now, the problem with that is that if you got the exposure and the incident part right, you might have less to do in the resiliency and the recovery side of the equation, but consequence is exactly that. We talk about microsegmentation in terms of access to network and network capabilities to exfiltrate or move data or information out.
We don't talk about things like microsegmentation for blast radius. How do I make a bad thing as small as possible when the bad thing happens? Because if I'm measuring exposure and interdiction, I should have a directional knowledge of where my exploitable weakness is. And this exposure, interdiction, and consequence universally applies across all ISO domains, all NIST domains, and it is intuitive for a number of organizations, but when we look at it from a frameworks and a standard standpoint and we start to try and look at it from an architecture standpoint, we've got architectures that are still supporting this giant monolithic framework of measuring the wrong things. So people are trying really, really hard over here, but they're fighting against a system that is actively interested in maintaining homeostasis. Nobody wants to go out and do some massive corporate reorganization around incentive rewards and evaluating their security solutions providers that are good enough that aren't making you safer from data.
Nobody wants to go do that because that's a huge uplift.
Den:
I wonder, do you think. I mean this whole compliance and governance, so governance risk compliance, that whole industry, I would suggest that if I look at all of these controls from NIST to CMMC to ISO to whatever, whatever, these things were created over a decade ago. And the things that they suggest you need to do in order to prove that your business is reducing risk, some of these things are bullshit. And I remember even years ago doing PCI audit and they're talking about your password complexity and I'm like, "Well, we went from passwords to passwordless for all of this classification of stuff and we're not changing passwords every 90 days." And this was two years before NIST updated their guidance on password rotation and complexity. So I look at it like there's a couple of problems. One is the vendors are busy creating the case for you needing to buy their ship.
The compliance in industry is busy saying you need to do all of this stuff and they're all making money from it, but they're not necessarily reducing risk. And I think this is the kind of point that you're getting at, which is we've built a machine and rewarded a machine that 20 years later perpetuates the same nonsense and it doesn't necessarily change anything. I mean, I look at it like, yeah, I'd rather stop a program than start a program.
Richard:
Well, I think that what gets missed, and you referenced it a little bit earlier, what gets missed is our history. If I asked any one of, I think the last number I saw is there's something like five million cybersecurity practitioners around the world today. If I asked a million of them, what's our history? Where did we come from? Where did accounts and passwords come from? How did we end up with NIST and ISO, which aren't really security? NIST is a quasi-governmental science lab. ISO is a Swiss engineering consortium, both great organizations, but why? Why didn't we ever create anything that was just like, it's security? Why did we always gravitate towards these models? And it's our history that is the reason why. Security didn't manifest one day in the digital world as security. It was IT operations. There wasn't a need for security in the 80s.
Everything was network isolated, mainframes, mid-ranges.
I'm certainly old enough to remember all of my customers having point-to-point connections. I got 400 payment processing customers. Every one of them has to have their own dedicated channel. If kids saw that today, they'd be like, "What the hell is that? Why don't you just use the internet?" But because of this isolation, the security demands were able to be managed by engineering staff that were associated directly with the operations of the stack. And when we got to, first of all, client server, which was a baby step in distributed computing, and then further on into what era we live in now, we took all those people that were basically like in most organizations, it was your Microsoft admins, and we said, "You are now security." And what are Microsoft admins worried about? Uptime, reliability, all of these operational metrics. What do our security metrics look like today?
They look more like uptime metrics than they look like security metrics.
Den:
I mean, that's also where we got that whole triad, right?
Richard:
Exactly, exactly. Mr. Schneider, the people process technology thing, I got to give Bruce credit. It has held. The problem
Den:
Is - I was thinking the other one, the confidentiality, integrity and availability. The
Richard:
CIA.
Den:
Yeah, the CIA one. But it is funny. It's like people and bloody acronym bingo, right? It's like, holy shit. The other thing is, Richard, I was thinking earlier as you were talking about in the early days, I mean, I look at hackers came out of telephone freaking or networking, and then you've got the server adminy people, people like you and I. I mean, I was doing identity in 92, like an ex-Novel. So I was like a Novell Sun directory before Microsoft even screwed all that bullshit up with make an active directory. So the reality is I look at it like, man, were we not talking about some of this crap in 1990? My first ever IT job, we were talking about things like this then. And to your point, we were just getting into the internet. So the security thing was a whole different game back then.
It's almost like I want to get a free long distance telephone connection because I didn't want to pay the stupid rates.
Richard:
Yeah. Well, real quick, public service announcement for hackers out there, and I've been guilty of this until I wrote this book, this is another thing that bad actors and adversaries took away from us. We should have never had the hoodie taken away from us and we should have never had the term hacker taken away from us. And a hacker at their core is somebody who's interested in how something works, pulls it apart, and if they're a good hacker, they put it back together again better than it was. That's a hacker. These folks that are wearing the hoodies and are being called hackers in the media are criminals. They are thieves.
They are murderers if we think about the impact that they're having on healthcare and shutting down emergency rooms. These are bad people. They don't deserve the hood or the hacker. Do not. But it's going to take us a while to wrestle that back from them. But the point you made I think is super interesting. And this book is meant to create the first substantial or substantive debate in cybersecurity in anybody's recent memory. We don't fight about anything in security at all. We just take everything as gospel. When was the last time that you were at a conference and you heard a pitch that was just so contrarian and so out of this world? Or was it like every pitch at that conference was just a variation on the same theme that we've heard about for the last 15 years? So when you said that, it kind of brought to mind, I remember my very first security project wasn't even a security project.
I did a Novel to Microsoft AD migration. And I remember the mandate on my project plan was we needed a hygiene Novel e-directory to make sure that all the accounts were the correct ones and nobody had more access than they were supposed to and so on and so forth. Nobody had access to printers that weren't in their department, all that nonsense. And then in 2009, what am I doing? Yelling at people for a dirty directory. In 2015, what am I? A dirty directory 2025, 2026. Look folks, if you're watching this thing and a problem that I experienced when I was 29 years old in the industry is still the same problem that contributes to over 80% of breaches and incidents, we got a problem and a technology solution ain't going to fix it.
Den:
Yeah. And this is where I love calling bullshit and stuff. And I remember talking to one of the leaders that reported to me at Adobe, this guy ran our whole SailPoint and all that stuff, which I know you're very familiar with these guys. And we were having this conversation just about least privilege and role-based access control. And I'm like, at the core, role-based access control is us saying that we're going to create a bunch of groups and you're going to be in the group because that's a role. And we're like, here's a role called engineers. I said, so someone has turned this thing into a big thing. I went, can we dial this bloody down a little bit? And it's like the core of it. The problem with the whole role-based bullshit is you end up with more groups than you do people. And it was really cool.
You'd run a script, it would analyze your environment and then it'd come back and it'd be like, this is what you need. And I'm like, I don't need that. I'm looking at it like we had 50,000 identities and then it wants to create 70,000 roles. I'm like, geez. I mean, complexity doesn't equal good security. So that was the other one is you look at all these vendors and all these solutions, they're very busy building more features and functions and telling you how you get more complex. At the end of it, I think the humans struggle to stay up on top of that complexity. So I kind of dialed shit back. I'm like, wait a minute, can we just pull this back a minute here? So I know we're whizzing through time. One of the things I'd love your take on this. So the book covers obviously what is wrong, a huge amount of evidence and data that talks about what's wrong.
What about the so what? What do we do about it? I've got to imagine at the end of the book there's aha, here's a recommendation. So what was your view on how do we turn this ship around?
Richard:
Yeah, very much so. I knew, and this is why it's taken so long to put this book together. I knew that I couldn't come out of the gate with a diagnostic like this if I wasn't at least attempting to present a remedy. So the last third of the book is definitely focused on, okay, how could we change it? Now, be frank, nothing in there is easy, not because it isn't easy to do if a corporation, a company, an agency has the political will and the economic interest to do it. It's just, again, we're talking about changing a massive ecosystem that is everything that's got us here were rational decisions based upon bad information.
And so that's a very difficult thing to unwind, but I think there's a lot of things to consider in the tail end of the book that orient towards how do we fix this? Certainly first and foremost among them is figuring out the means and methods to measure whether we're getting safer from one day to the next, right? Our attack and exploit surfaces reducing, are newly manifested vulnerabilities that represent an immediate threat, not necessarily a zero day because zero day is now negative seven days, by the way. What are the response rates? How fast are we remediating? Not how many are we remediating? These measures, when people start to think about them, and this goes back to the peer readers that have read this book, and for the audience at home, if there's a cybersecurity name that you've heard of in the industry, they probably were a peer reader for this book.
And what happened, somebody said that they were going to start calling the Morpheus because when you start to see the basis for these kind of security and outcome performance metrics, you can't unsee them. All of a sudden you realize, oh my gosh, that's why this measure has always been worthless and I've always felt it with worthless. And Lord, I hated reporting it to the board because it didn't mean anything about whether we're safe or not. The other thing that's in there, and I think this is a really, really important point, is that in every industry, in every movement that has an obligation for safety and security of human beings, there has always been an epiphany that has caused those industries to change what they're doing. The airline industry is number one. For years and years and years as more air travel kept booming through the 60s, 70s and 80s, the airline industry was having a tremendous difficulty understanding how to mitigate the crashes that were happening.
And at some point, and there's a lot of this in the book, at some point we created the National Traffic Safety Board and we began investigating airline crashes. And if you look at how the airline industry works today, the airline industry does not build an airplane to guarantee that it lands safely every single time. The airline industry builds airplanes that do not have catastrophic failures when one simple thing breaks. Now that sure sounds a hell of a lot like cybersecurity and the one person with the Microsoft account, this has happened in industrial safety. Shit, it happened in elevators in the 1890s with safety breaks. At some point, the thinking moves to how do we produce safety and security and security or safety engineering is a full discipline and we can adopt it and embrace it. And before anybody throws up their hands and goes, well, first of all, it's digital, it's not that big of a deal.
Go chase anybody that's tracking down how many people are actually dying physically because of hospital hacks or because of traffic light hacks or because of. And then go track down the 87,000 people in the identity theft resource center whose lives are being destroyed by bad actors while companies are taking pre-tax write-offs for their cyber losses. We are screwing everything up because we're not focused on how to change it. And when we look at the security and safety engineering side, people can throw up their hands and say, "Well, that'll just be too hard." Except Jen Easterly was already trying to do it with the Cybersecurity Review Board.
She was already trying to make the case that if we evaluated and looked at Microsoft's massive breach, we can learn lessons from it. And in learning lessons, we can propagate those lessons to the rest of the world and the rest of the world can become safer. And the last thing that I'll say about that improvement space is there will be a lot of people, a lot of cynical people who will say, "Well, you know what? The companies and the legal industry will never allow it to happen because if you have to produce a forensic report about how I got breached so that it can be shared with your industry colleagues so there's no more nonsense about what best practices are, I can actually focus on most effective practices because I know how to fix that problem," then you're just giving the lawyers on the class action side all the ammunition saying that you were negligent.
Well, let's look at the airline industry. How did they avoid that? Simple. The NTSB says that any aircraft investigation and its outcomes cannot be used as litigation evidence. That is federal law. And by the way, they don't need that evidence anyhow. They're going to sue your ass and they're going to win.
I know because I've looked at all the class action lawsuits and litigation that have been won against companies that have had cyber incidents and events. So it's a bullshit argument that we're not going to disclose with each other how we're getting hacked. Instead, we're going to go back to NIST NYSO and go, "Well, did I do this thing? Did I do this thing? Did I do this
Den:
Thing?"
You struck a nerve there. Using the word best practices is almost like using the word common sense. They're neither best nor they're common. And I think best practices were really invented by vendors that said, "This is the best practice to deploy my thing in a way that secures your thing." And at the end of it, for me, it really is, I kind of just go back to this jobsworth bullshit. It's like someone is like, "Wait a minute, if I write all this shit up, then that's the right pontificating." I think a lot of these people, there's so many people that just pontificate on shit and they write all this stuff. And that's why for me, it's like all the governance risk, all the standards and all these things and all the best practices and all that, it's like, I don't know, have you tried to deploy some of the shit that you're talking about sometimes at scale in a way that actually reduces the risk?
And I've had conversations with people over the years. I remember talking about zero trust and all this stuff, and I remember at the end of it someone said, "Well, that's not really zero trust." And I'll not name his name because he's quite an influential character. But the reality was it's like, well, it might not be the term, might not be the thing that you are getting at, but I'll tell you what it is. It's reducing the risk for our business in a way that makes financial sense for us. Because for me to do all the things that someone says makes that definition real here, it would be another million dollars more. And it's like, well, we're not going to spend another million dollars more. People forget the cost of solving the problem. Should it be more or less than the cost of the problem itself?
Yeah. That is an equation that I think a lot of people forget about.
Richard:
So I have built all of the business economics math, and that's also in the last part of the book, the business economics math that turns cybersecurity into an actual business function. If you eat another myth that cybersecurity is just a cost of doing business, which again, I can say that in a room and 3000 people can repeat it back to me because that's what we say in cybersecurity, then you're basically saying that I am one of only two corporate costs of goods sold, and that is us and corporate taxes. We are saying we provide no economic benefit and you have to spend money on us anyhow, whether you want to or not. And to be honest with you, the cyber insurance industry as well as the standards industry, as well as the federal regulatory industry have guaranteed that. They say you have to have a security program.
They say that you have to have certain solutions in place. They say that you must invest more money on a system that we've already confirmed is built measuring the wrong thing. So we create this massive self-perpetuating machine. And the truth is that when we peel that apart, the means to measure us financially on equal terms with all other parts of the business have always been there. We haven't done it, and that doesn't mean that nobody's ever done it. I want to just briefly share that there is an entire piece in the book about the business economics, incentive and reward structures, compensation structures that are based upon performance, not whether you got breached or not, but whether or not you keep letting Jeff crack open production every time with those stash credentials and you don't fire him because by God, if we got rid of him, the whole system would go down.
Those are, again, not risks. Those are business decisions and they're bad ones. And so when we look at that and we look at things like unit costing down to the actual OS and stack rack level, whether it's virtual racks or physical racks, I didn't invent that. I learned that at JP Morgan Chase. We unit costed everything, including security. So guess what? I was able to one day convince somebody who's pretty famous in the banking industry that it wasn't enough that I was charging people for manual password resets, and it was $8.37 per, because it required a human body. I convinced them to let me charge a risk premium. Why? Because a manual password reset was way riskier than an automated password reset on my platform, and it was way cheaper. But 8.37 versus 17 cents wasn't enough to move that business leader to get off their dead ass and get on my platform because they needed to pay for engineering.
They needed to take people out of the loop that needed to work on that and get it done. And we're working on features. So when I walked into that guy's office and I said $28.37, and by the way, this is a budget true up. You need to pay for it for the remaining six months of this fiscal year, not in next year's forecast. You know who moved faster than Lightspeed to my platform? That dude that was going to pay 28.37. And I learned that at Chase. It is not impossible. It is a matter of will and interest economically to change things. And more importantly, and this is a good wrapping off point, I'm not doing this because I'm selling anything. I'm not doing this because I'm building an entire new way to certify people for security. There'll be a framework. I don't think I'll ever do anything with it, but have it out there so people can test the metrics to see if they actually work because I don't know if they do.
It's conceptual. But what I believe in, and this just comes from how I grew up, it came from working for my dad from the time I was 12 years old. I believe that stewardship is important. I believe that companies used to take serious the responsibility to protect their customers, to make their customers' lives better and easier. We can be as cynical as we want to about how the digital age has changed that, but when we are pushing the cost of catastrophic consequences down on people that are our customers, our citizens, and we are getting to trot off and take pre-tax expenses on our cyber losses, and they'll go crow about how good our security got because we spent another $20 million on security solution providers who are measuring the wrong thing, this is wrong. We need to be responsible for what we've been entrusted with, and that is a serious obligation.
And when we don't take that obligation seriously, we see the kind of spiraling that we're seeing in today's society and culture. So this is so much bigger than cybersecurity because if I can trust my digital things with someone, then I can trust that they're out looking out for my best interests.
Den:
Yeah. And I love wrapping on that, Richard, because here's the one statement that we always hear when someone gets breached is the CEO says, "We take security really seriously." We're like, "Really? We do."
Richard:
Now.
Den:
We take it really seriously now. But I've never heard a CEO wake up in the morning and think, "I'd love to spend more money on security." This doesn't bloody happen. We haven't given a
Richard:
Reason to. We haven't given them a reason to, right?
Den:
Yeah.
Richard:
Because we're not measuring what we're doing on a CEO's or a CFO's terms. We can't talk to them in their language. We can change that though.
Den:
Yeah. Yeah. And actually, same funny conversation I had with a client just over the last couple of weeks was you keep saying there's no budget to do the thing where you've not presented the data in a way to the CFO that enables him to understand the thing you're proposing, the risk it reduces, why it does that thing, and blah, blah, blah, blah, blah. If you don't present it in a way that they can understand, they can't make a decision. And we kind of screw that up a little bit. Thank you very much. One thing I want to close with, you and your son, you're the only father-son duo that's done conference talks at RSA. I think you've done two now. I did talk to you several times over the years about you guys coming on the show, so I want to tease that one up.
The book is out. When is the book out?
Richard:
So goal is going to be mid to end of October, Cybersecurity Awareness Week, but not the first couple of weeks because everyone will just be sending out press releases for you to change your passwords. So it's a whole month long, so I though I'd try and give somebody some meat at the end.
Den:
The
Richard:
Best way to sign up for pre-launch information is go to hackerinahoodie.com. There's also a ton of information about the economics of the bad guys and adversaries versus the good guys. So that'll be a long going project for me. And then the goal is that we'll be dropping a lot of nuggets about this over the course of the next five to six weeks, but it's like Chicago, vote off and vote early. For all of you that are listening, sign up for the pre-launch early, deal with my newsletters when they come out and jump on buying at the first day. There have only ever been two cybersecurity practitioner bestsellers in history.
Den:
Oh, really?
Richard:
Yeah, which I think is fascinating.
Den:
We might have a third, and we'll put all the links in the show notes and stuff like that as well. So we'll definitely have that. Hey Richard, thank you very much, man. It's always great catching up with you. Normally we catch up at the conferences and we manage to get a sneaky little drink in. So this is probably one of the rare moments where we're not sitting shooting the shit over the beer.
Richard:
Agreed.
Den:
So hey bud, thank you very much. I appreciate it. Great talking as always. And yeah, we'll follow up. I want you and your son on the show. And then yeah, folks, this is a disruptive book and I think it really pulls apart some of our failings over the last 30 plus years. So thank you very much, Richard. Everybody, Richard Bird.
Narrator:
That wraps up this episode of 909 Exec. If you found value here, subscribe and leave a rating to help others discover the show. To learn more about 909 Cyber, our advisory services, and how we help organizations secure growth, visit 909cyber.com. Thanks for listening. And until next time, lead with clarity, build trust, and stay secure.


